Główny Inspektorat Sanitarny Awards PLN 32.5M Cybersecurity Contract
Winning B2B Cybersecurity, IT Services, and Public Sector Tenders in Poland & Europe
Standfirst:
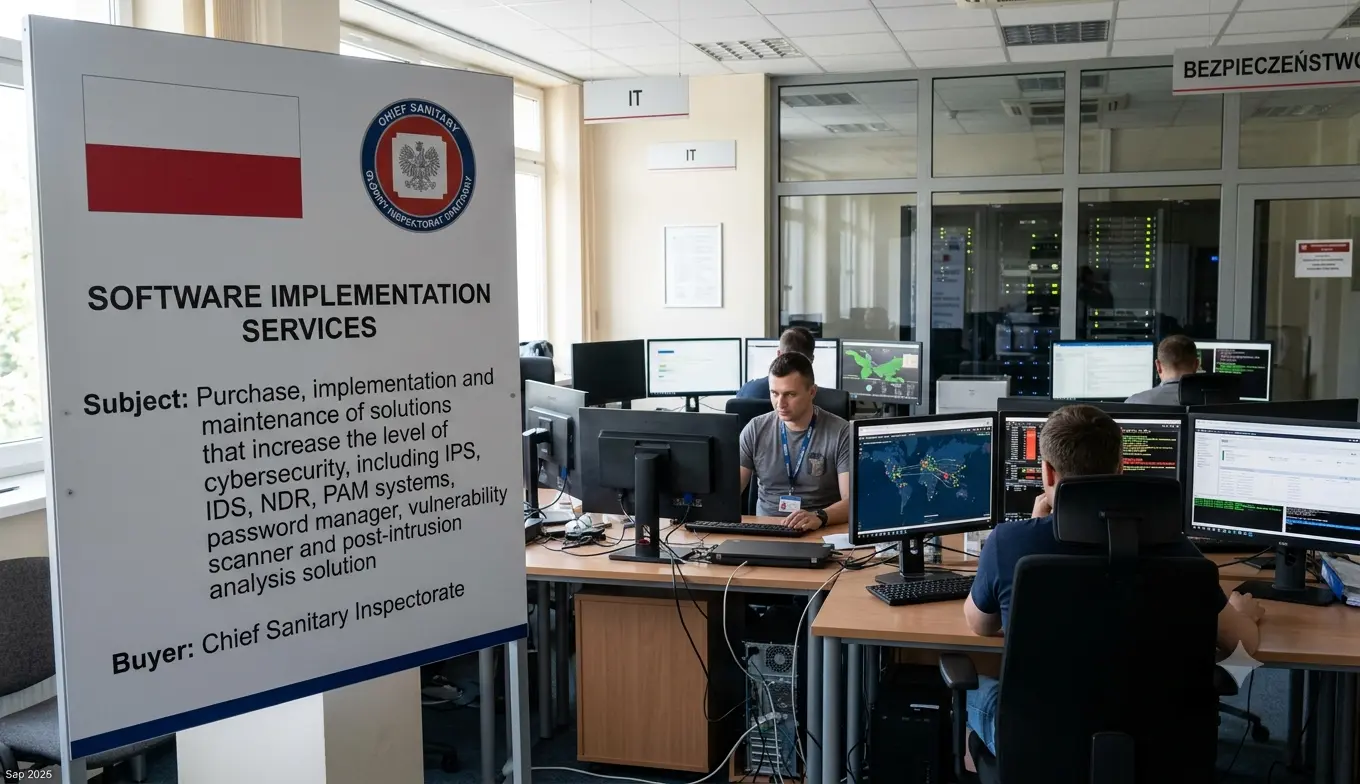
Poland has published the results stage of a major cybersecurity procurement covering seven technology areas for the Chief Sanitary Inspectorate and subordinate border sanitary and epidemiological stations. The procurement covers implementation and maintenance of IPS, IDS, NDR, PAM, password management, vulnerability scanning and post incident analysis solutions. Six lots remain in an ongoing competition, while the third lot closed without receiving any tenders. The project is being financed with European Union funding under Poland's National Recovery and Resilience Plan and is intended to increase the institutional cyber resilience of units of the State Sanitary Inspection.
Introduction
Poland's Główny Inspektorat Sanitarny, or Chief Sanitary Inspectorate, is progressing with a multi lot procurement designed to strengthen cybersecurity capabilities across the State Sanitary Inspection network. TED publication 642655-2026 identifies the procurement as a services contract for the purchase, implementation and maintenance of cybersecurity solutions covering several complementary security functions. The procurement is divided into seven lots, allowing suppliers to bid for individual technology areas rather than requiring a single solution across the entire programme. The notice states that the project is being implemented for the Chief Sanitary Inspectorate and nine subordinate border sanitary and epidemiological stations.
The procurement is part of the project titled “Zwiększenie instytucjonalnej cyberodporności jednostek Państwowej Inspekcji Sanitarnej”, translated as increasing the institutional cyber resilience of units of the State Sanitary Inspection. The notice links the project to the European Union funded National Recovery and Resilience Plan, specifically Priority C3 Cybersecurity and Measure C3.1.1 Cybersecurity, known as CyberPL.
Why This Contract Matters
The procurement is significant because it approaches cybersecurity as a collection of connected capabilities rather than a single software purchase. The seven lots address prevention, detection, privileged access, password management, vulnerability identification, network monitoring and post incident analysis. Together, these functions cover multiple stages of an organisation's cybersecurity operating environment.
For public health institutions, strengthening digital resilience can support the continuity and protection of information systems used by administrative and operational units. The procurement also has a distributed implementation dimension because the notice identifies multiple subordinate border sanitary and epidemiological stations as beneficiaries of the project. This creates a broader institutional requirement than a solution intended only for the central authority.
Contract Timeline
The procurement carries internal identifier 17/2026/P and procedure identifier 8f5c05d4 6a14 4a51 8278 08ffd8b13a7a. The previous notice associated with the procurement is 575843-2026. TED publication 642655-2026 was published in Official Journal S issue 180/2026 on 17 September 2026 after being dispatched on 15 September 2026.
The procurement uses an open procedure and is not identified as an accelerated procedure. Each of the seven lots has an estimated duration of 1,141 days. The current result notice does not record completed winner selection for six lots and records no winner for Lot 3 because no tenders were received.
Contract Overview
The procurement covers software implementation services under main CPV code 72263000, Software implementation services. Additional classifications are CPV 48000000 for software package and information systems and CPV 48517000 for IT software package. The place of performance is Warsaw, Poland, within the Miasto Warszawa NUTS region PL911.
Rather than creating a framework agreement or dynamic purchasing system, the contracting authority is procuring the seven defined lots directly through the open procedure. The notice states that partial offers are permitted and suppliers may submit offers for any number of lots, with no maximum number of lots that can be awarded to the same supplier.
Key Contract Details
| Detail | Information |
|---|---|
| Country | Poland |
| Contracting Authority | Główny Inspektorat Sanitarny |
| Procurement | Purchase, implementation and maintenance of cybersecurity solutions |
| Procedure | Open procedure |
| Internal Identifier | 17/2026/P |
| Number of Lots | 7 |
| Main CPV | 72263000, Software implementation services |
| Additional CPVs | 48000000, 48517000 |
| Location | Warsaw, Poland |
| Lot Duration | 1,141 days |
| Funding | European Union funds through the National Recovery and Resilience Plan |
| GPA Covered | Yes |
| Framework Agreement | No |
| Dynamic Purchasing System | No |
| Current Result Status | Six lots ongoing; Lot 3 closed without tenders |
Project Scope
The first lot concerns an Intrusion Prevention System, or IPS, intended to detect and block attacks in real time. The second lot covers an Intrusion Detection System, or IDS, focused on detecting intrusions, monitoring network traffic, analysing known threats and identifying suspicious activity or anomalies. These two areas provide complementary capabilities for monitoring and responding to network security events.
The third lot covers post incident analysis software intended for active testing of computer systems, networks or applications to identify weaknesses that could potentially be exploited for unauthorised access or attacks. The fourth lot concerns a central password management solution for secure management, storage and transfer of passwords together with technical support.
The fifth lot covers Privileged Access Management, or PAM, together with technical support. The sixth concerns vulnerability scanning software for automated identification of vulnerabilities in information and communications technology infrastructure. The seventh covers Network Detection and Response, or NDR, for network monitoring and threat response together with technical support.
About the Contracting Authority
Główny Inspektorat Sanitarny is the contracting authority named in the TED notice. The organisation is classified as a body governed by public law and its contracting authority activity is identified under the health sector. Its registered address is Targowa 65 in Warsaw.
The procurement is intended not only for the central organisation but also for nine subordinate border sanitary and epidemiological stations located in Dorohusk, Elbląg, Gdynia, Hrebenne, Koroszczyn, Przemyśl, Suwałki, Szczecin and Warsaw.
About the Organisations Involved
Główny Inspektorat Sanitarny is the buyer and the principal public organisation responsible for the procurement. The notice gives its registration number as 5252147194 and identifies its Warsaw headquarters at Targowa 65.
Krajowa Izba Odwoławcza is identified as the review organisation and as the organisation providing information on review procedures. It is based at ul. Postępu 17 in Warsaw and is associated with the procurement's formal review arrangements.
Publications Office of the European Union is identified in the notice as the TED eSender. The organisation is based in Luxembourg and is responsible for the publication infrastructure through which the procurement notice appears in the Official Journal of the European Union.
The notice does not identify a successful supplier for the six lots that remain open and therefore no awarded supplier should be named for those lots. For Lot 3, the notice explicitly records that no tenders, requests to participate or projects were received.
Procurement Analysis
The structure of this procurement indicates an effort to separate major cybersecurity functions into clearly defined procurement packages. This allows suppliers with specialised capabilities to compete for relevant lots while giving the contracting authority flexibility to source different categories of technology independently. The notice expressly permits partial bids for any number of lots.
Another notable feature is the common CPV classification across the lots. Each lot uses software implementation services as its main classification with software package and information systems and IT software package as additional classifications. This reflects the fact that the procurement is not limited to supplying software products but also includes implementation and related support requirements.
The procurement is also designed around a relatively long delivery period of 1,141 days for each lot. This creates a service component alongside implementation and means suppliers need to consider the ability to support the solutions throughout the stated contract period.
Additional Procurement Facts
The procurement is covered by the Government Procurement Agreement. The notice also confirms that it does not involve a framework agreement or dynamic purchasing system. Price is identified as the award criterion with a 100% weighting for each lot, with detailed methodology referred to in the procurement documents.
The authority does not permit variant offers and does not provide for an electronic auction. It also permits equivalent solutions where the procurement documentation identifies trademarks, patents, origins, sources or specific processes, provided the proposed equivalent meets the requirements specified in the description of the subject matter of the procurement.
Market & Industry Perspective
The procurement demonstrates how public sector cybersecurity programmes can be divided into specialised technology categories. IPS, IDS and NDR address different aspects of network security, while PAM and password management focus on access control. Vulnerability scanning addresses identification of weaknesses and post incident analysis addresses activities following security events or security testing.
For the cybersecurity technology market, this type of procurement can create opportunities for software vendors, implementation partners, systems integrators and technical support providers. Because suppliers can submit bids for individual lots, participation does not necessarily require a company to provide every capability listed in the overall procurement.
The procurement also highlights the importance of implementation services. The principal CPV is not simply a software product classification but software implementation services, while the procurement description repeatedly combines technology acquisition with implementation and technical support.
Economic Significance
The notice does not state a total contract award value because the procurement has not reached completed award status for the six ongoing lots. Accordingly, no overall awarded value should be attributed to this notice.
Its economic significance instead comes from the scale and breadth of the technology programme and its EU funding connection. The project is financed through the National Recovery and Resilience Plan under the cybersecurity component identified in the notice.
Future Procurement Opportunities
The current procurement status provides an important signal for suppliers tracking Polish public sector cybersecurity opportunities. Six lots remain listed as ongoing, covering IPS, IDS, password management, PAM, vulnerability scanning and NDR. Companies monitoring these categories should therefore distinguish this notice from a conventional completed award notice.
Lot 3 may also be relevant for future market monitoring because it closed without receiving tenders. The notice identifies the subject as post incident analysis software and records that no tenders, requests to participate or projects were received.
Future procurement activity may also emerge around maintenance, upgrades, renewals, additional security capabilities or related implementation services as public institutions continue developing cyber resilience programmes. The present notice alone, however, does not confirm any future procurement dates or contracts.
Opportunities for Suppliers
Suppliers specialising in one or more of the seven cybersecurity categories can assess the procurement on a lot by lot basis. The authority allows offers for any number of lots and does not set a maximum number of lots that may be awarded to the same supplier.
The project also creates opportunities for suppliers capable of combining software implementation with continuing technical support. Companies considering participation should review the official procurement documentation and the detailed requirements in the relevant description of the subject matter and draft contractual provisions.
What Businesses Should Watch
Businesses should first watch the status of the six lots still shown as ongoing in TED. The result section does not identify winners for these lots, so suppliers and procurement intelligence teams should avoid treating the publication as a final award announcement.
Second, businesses should monitor any subsequent notice concerning Lot 3 because the current publication records no tenders. A subsequent procurement or revised approach could create a new opportunity, although the present notice does not confirm that such a procurement will occur.
Finally, suppliers should pay attention to the implementation and support requirements rather than viewing the procurement solely as a software licensing opportunity. The common CPV structure and the descriptions across the seven lots indicate that implementation is a central part of the procurement.
PolandTenders.com Procurement Intelligence
From a procurement intelligence perspective, this notice illustrates a broader shift toward modular cybersecurity procurement in public institutions. Instead of sourcing one broad cybersecurity platform, the authority has structured the requirement around distinct security capabilities that can be procured separately. This structure gives specialist technology providers an identifiable entry point into a wider public sector programme.
The strategic importance of the procurement is also visible in its funding model. The project is connected to the National Recovery and Resilience Plan and specifically to the cybersecurity component of the programme. That connection shows how EU backed investment can translate into technology procurement across public institutions and their subordinate units.
For suppliers, one of the clearest lessons is the value of precise positioning around individual cybersecurity capabilities. A company does not necessarily need to offer every technology listed in the overall procurement because the contracting authority has expressly permitted partial offers across the seven lots. This can allow specialised vendors and implementation partners to identify the lot that most closely matches their product and service portfolio.
Supplier positioning should also account for the complete delivery lifecycle. The procurement descriptions combine acquisition and implementation with support in several technology areas, while each lot carries a duration of 1,141 days. Suppliers therefore need to assess their ability to provide implementation resources and sustained technical support rather than focusing only on the initial software component.
Looking ahead, similar public sector cybersecurity procurements could increasingly combine network monitoring, identity and privileged access controls, vulnerability management and incident analysis within coordinated programmes. Whether future procurements use the same seven lot structure will depend on individual contracting authorities and their requirements, but this notice provides a useful example of how a public institution can divide a large cybersecurity requirement into specialised procurement categories.
Supplier Takeaways
- Track all seven lots separately because their procurement outcomes are not identical.
- Six lots are currently shown as ongoing and do not have selected winners in this notice.
- Lot 3 closed without receiving any tenders, requests to participate or projects.
- Partial bidding is permitted and suppliers may bid for any number of lots.
- The award criterion for each lot is price with a stated 100% weighting.
- The main CPV is 72263000 for software implementation services.
- Implementation and technical support are important components across the procurement.
- The stated duration for each lot is 1,141 days.
- The procurement is funded through an EU backed National Recovery and Resilience Plan cybersecurity project.
- Suppliers should review the detailed SWZ and technical specifications before assessing eligibility or bid strategy.
Key Takeaways
- Buyer: Główny Inspektorat Sanitarny.
- Country: Poland.
- Location: Warsaw, Poland.
- Procurement: Cybersecurity software purchase, implementation and maintenance.
- Lots: Seven.
- Technology areas: IPS, IDS, post incident analysis, password management, PAM, vulnerability scanning and NDR.
- Procedure: Open procedure.
- Main CPV: 72263000, Software implementation services.
- Additional CPVs: 48000000 and 48517000.
- Duration: 1,141 days per lot.
- Funding: European Union funds through the National Recovery and Resilience Plan.
- GPA: Yes.
- Framework agreement: No.
- DPS: No.
- Current result: Six lots remain ongoing and one lot closed without tenders.
Conclusion
Poland's seven lot cybersecurity procurement represents a broad digital resilience programme for the Chief Sanitary Inspectorate and its subordinate border sanitary and epidemiological stations. The current TED result notice should be understood as a procurement status update rather than a completed contract award, with six lots still ongoing and Lot 3 closed without tenders.
For cybersecurity suppliers, the procurement provides a clear view of the technology categories being addressed and demonstrates the opportunities created by EU supported public sector cyber resilience investment in Poland.
Source: TED, Contract or concession award notice, publication 642655-2026, OJ S 180/2026, published 17 September 2026.
Frequently Asked Questions (FAQs)
Fresh and verified Tenders from Poland. Find, search and filter Tenders/Call for bids/RFIs/RFPs/RFQs/Auctions published by the government, public sector undertakings (PSUs) and private entities.
- 1,000+ Tenders
- Verified Tenders Only
- New Tenders Every Day
- Tenders Result Data
- Archive & Historical Tenders Access
- Consultants for RFI/RFP/RFQ
- Tender Notifications & Alerts
- Search, Sort, and Filter Tenders
- Bidding Assistance & Consulting
- Customer Support
- Publish your Tenders
- Export data to Excel
- API for Tender Data
- Tender Documents
Fill out the form below and you will receive a call from us within 24 hours.
Get FREE SAMPLE TENDERS from Poland in your email inbox.
Copyright © 2014-2026 PolandTenders.com. All Rights Reserved.